RudyDesk Security: What Is Protected, What the Server Sees and What Is Up to You
Letting someone into your computer is a serious decision. Here, point by point: what is protected technically, what our server sees and what stays in your hands.
What the server sees and what it does not
The server exists so that two devices can find each other. After that, screen, audio, files and input go directly between them. If a router blocks the direct path, data goes through a relay, but the relay passes it encrypted and cannot read it.
The server keeps a security log: device number, IP address and connection time. It protects against password guessing and helps investigate incidents; it is limited in size and overwritten in a loop. Session content — screen, keystrokes, files — is not recorded anywhere.
Encryption
- Screen, audio and data are protected by DTLS-SRTP: the keys are created on the devices, the server does not have them
- The remote command line is encrypted separately: the key is derived with ECDH, commands use AES-256-GCM, with fresh keys for every session
The password never reaches the server
New versions of the app do not send the device password at all. The person connecting proves they know it by answering a one-time challenge; an intercepted answer will not work twice.
Guessing is stopped: after 5 failed attempts — a 5-minute pause, after 15 — an hour, after 30 access is closed and only the machine itself can lift the block.
Nobody connects without your consent
Every connection must be confirmed on the computer. If the request comes from an unknown device, the window warns about scammers: real banks and support services never ask for remote access over the phone.
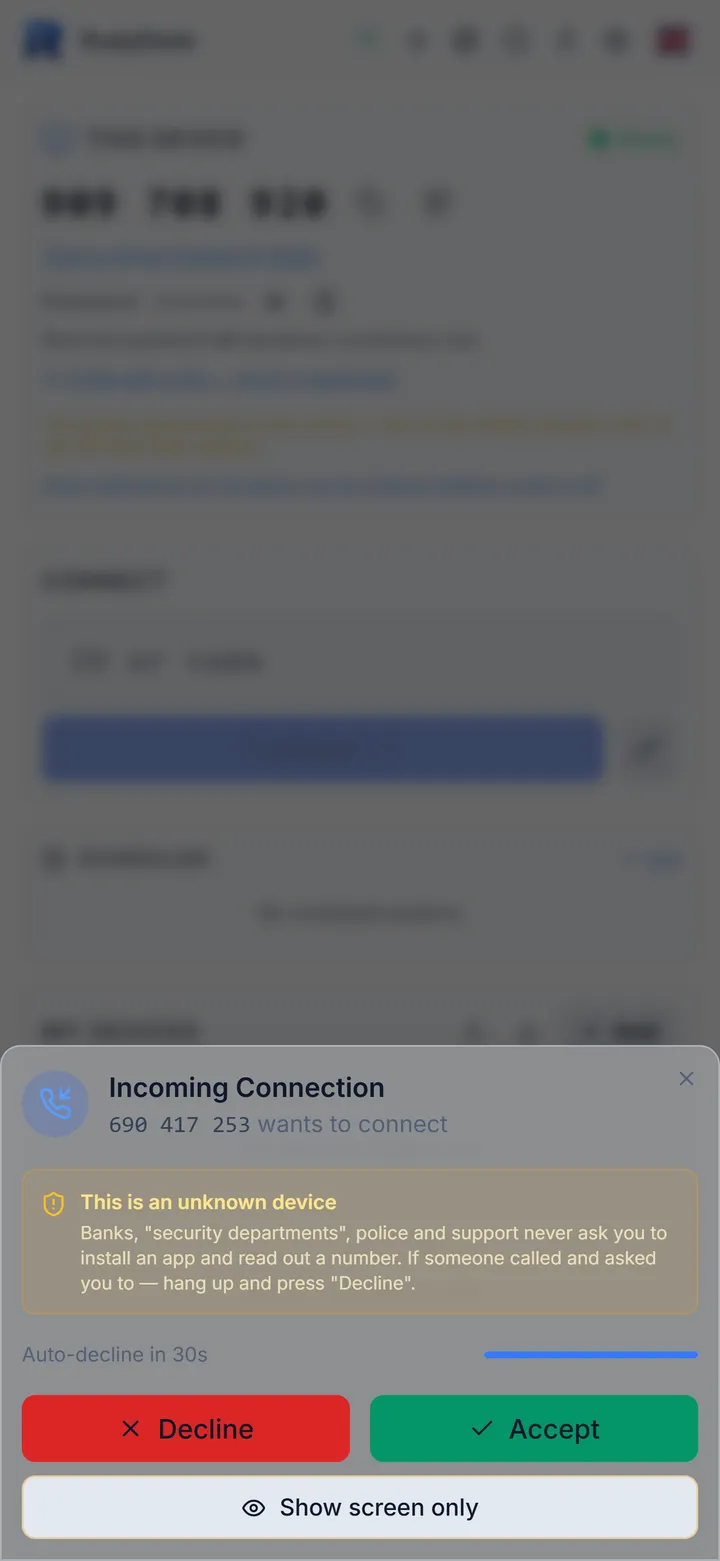
The "Show screen only" button allows looking but not touching: mouse, keyboard, files, clipboard and terminal are off limits. The computer itself enforces this, not the other side's app.
Invite link
You can send a link instead of a number and password. It works once, lives 15 minutes and is wiped from the address bar right away. You still have to confirm the connection.
Session code
Next to the lock on the session toolbar is a short code. The devices compute it from the encryption keys, and it never passes through the server. Read it to the other person over the phone: if the codes match, nobody is sitting between you.
Activity log
The owner sees who connected, when and for how long, and under each entry — what was done: which files were received, whether the terminal was opened, whether the clipboard was used. Keystrokes and pasted text are not recorded — that would be surveillance, not a log.
Two-factor sign-in and access lists
TOTP is supported — Google Authenticator, 1Password, Aegis and others. Turning it on gives you five recovery codes: write them down in case you lose your phone. You can set a whitelist: only the listed numbers can connect, everyone else is refused without your involvement.
Signed updates
Every update is signed with the RudyDesk key. The app checks the signature and SHA-256 before installing and refuses a tampered file. The fingerprints of all files are published on the download page.
What is up to you
- Never allow a connection to someone who called you and claimed to be a bank or "tech support"
- Use a long password that differs from your other sites
- Turn on two-factor sign-in on a machine that is accessed while you are away
- If in doubt, allow screen viewing only